AI News
08 Oct 2026
Read 8 min
AI safety tips for small businesses to prevent breaches
AI safety tips for small businesses to cut breach risk and safeguard customer data with simple steps
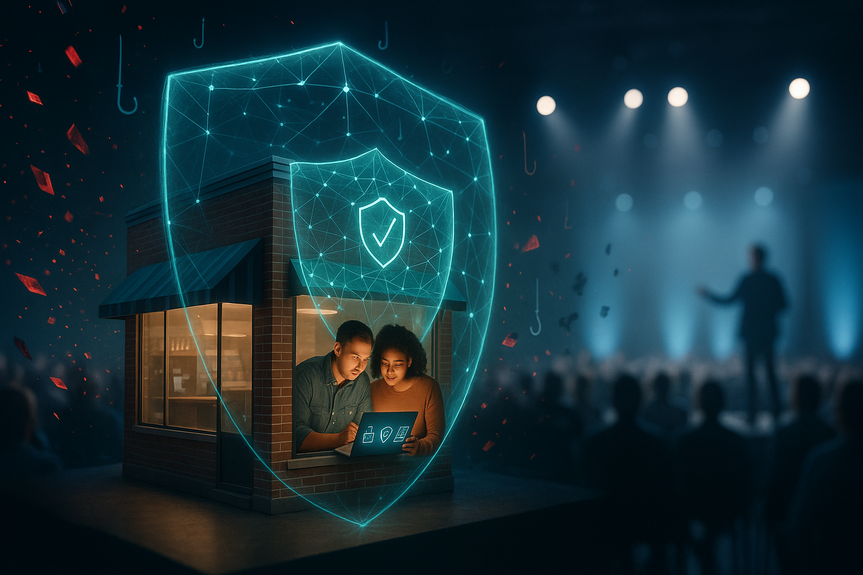
Use these AI safety tips for small businesses to cut breach risk while keeping speed. Do not paste sensitive data into chatbots, enforce MFA and passkeys, train staff on AI scams and deepfakes, vet vendors, patch and back up systems, and set a clear AI use policy. Start with low-cost, high-impact steps today.
Artificial intelligence can help small teams work faster, but it also gives attackers new tools. Security leaders urge owners to share less personal data with AI tools and to build simple guardrails. Even if you cannot match a big company’s budget, you can make smart choices that lower risk right now.
Why AI can help and hurt small firms
AI can write drafts, summarize notes, and sort data. It also helps defenders spot threats faster. But criminals use AI to send smarter phishing emails, fake voices, and malware at scale. The result: more attacks, faster attacks, and wider reach. That is why you need clear rules and steady basics.AI safety tips for small businesses
Protect sensitive data in prompts
- Never paste Social Security numbers, bank details, health data, or customer lists into public chatbots.
- Use placeholders instead of real values (for example, write “SSN” or “account_number”).
- Turn off chat history and model training when possible, or use enterprise versions with data controls.
- Sanitize and redact files before upload; keep a clean “share” copy separate from the source.
- Log what data goes into which tool; review access monthly.
Lock down accounts and devices
- Enable multi-factor authentication (MFA) or passkeys for email, cloud apps, and AI tools.
- Use single sign-on (SSO) and least-privilege access; remove unused accounts fast.
- Keep separate admin accounts; do not browse or chat with admin rights.
- Encrypt laptops and phones; install endpoint protection and turn on device auto-lock.
Train your people against AI-powered scams
- Run short, monthly phishing drills; teach staff to slow down and verify.
- Set a voice/video “safe word” for money or password requests to fight deepfakes.
- Require call-backs to known numbers before paying invoices or sharing codes.
- Flag external emails and look for small changes in domains and bank info.
Manage vendors and AI tools
- Keep an approved list of AI apps; block unvetted tools (“shadow AI”).
- Review privacy terms: data retention, training opt-out, storage location, and breach notice.
- Ask for basic security proofs (SOC 2/ISO 27001) when handling customer data.
- Use data processing agreements if vendors handle PII; check HIPAA/PCI triggers.
- Sandbox external content and links to reduce prompt injection and malware risk.
Keep systems patched and backed up
- Turn on automatic updates for OS, browsers, plugins, and AI desktop apps.
- Patch third-party software monthly; fast-track critical fixes.
- Follow 3-2-1 backups (3 copies, 2 media, 1 offsite); add an immutable backup.
- Test restores quarterly so you know recovery time and that backups are clean.
Write a simple AI use policy
- State what data is okay to share, which tools are allowed, and where outputs can be stored.
- Require human review before sharing AI-generated content with customers.
- Ban uploading secrets: API keys, passwords, and private code.
- List who to contact if data is exposed or an account is taken over.
Prepare an incident response plan
- Create playbooks for data leaks through AI, account takeovers, and vendor breaches.
- Steps: isolate the account/device, revoke tokens, reset passwords, and check logs.
- Notify affected customers when required; record actions and lessons learned.
Budget-friendly steps for the first 30 days
- Enable MFA/passkeys on email, finance apps, cloud storage, and AI tools.
- Publish a one-page AI policy and an approved tools list.
- Train staff for 20 minutes on safe prompts and phishing red flags.
- Turn off chat history/model training where possible; review vendor settings.
- Set automatic updates; run a full backup and test a file restore.
Metrics that prove progress
- Percent of accounts with MFA/passkeys enabled.
- Phishing simulation failure rate month over month.
- Time to apply critical patches.
- Number of approved tools vs. blocked “shadow AI” apps.
- Backup restore success rate and recovery time.
For more news: Click Here
FAQ
Q: What immediate steps should small businesses take to protect sensitive data when using AI tools?
A: Never paste Social Security numbers, bank details, health data, or customer lists into public chatbots; use placeholders and turn off chat history or model training when possible. Sanitize or redact files before uploading, keep a clean share copy separate from the source, and log what data goes into each tool for monthly review.
Q: How can small businesses secure accounts and devices used with AI?
A: Enable multi-factor authentication or passkeys for email, cloud apps, and AI tools, use single sign-on with least-privilege access, and remove unused accounts promptly. Keep separate admin accounts, encrypt laptops and phones, install endpoint protection, and enable device auto-lock to reduce exposure.
Q: What training should employees receive to defend against AI-powered scams and deepfakes?
A: Run short, monthly phishing drills and teach staff to slow down, verify requests, and flag external emails for domain or bank-info changes. Use a voice or video safe word for money or password requests and require callbacks to known numbers before paying invoices or sharing codes.
Q: How should small firms manage vendors and “shadow AI” tools safely?
A: Maintain an approved list of AI apps and block unvetted “shadow AI” tools while reviewing vendor privacy terms for data retention, training opt-out, storage location, and breach notification. Ask vendors for security proofs such as SOC 2 or ISO 27001, use data processing agreements when they handle PII, and sandbox external content and links to reduce prompt injection and malware risk.
Q: What should an AI use policy for a small business include?
A: State what data is acceptable to share, which tools are allowed, and where outputs can be stored, and require human review before sharing AI-generated content with customers. Ban uploading secrets like API keys, passwords, or private code and list who to contact if data is exposed or an account is taken over.
Q: What patching and backup practices are recommended to protect against AI-related threats?
A: Turn on automatic updates for operating systems, browsers, plugins, and AI desktop apps, and patch third-party software monthly while fast-tracking critical fixes. Follow a 3-2-1 backup strategy (three copies, two media, one offsite), add an immutable backup, and test restores quarterly to verify recovery.
Q: How should small businesses prepare an incident response plan for AI-related breaches?
A: Create playbooks for data leaks through AI, account takeovers, and vendor breaches with clear steps to isolate affected accounts or devices, revoke tokens, reset passwords, and review logs. Notify affected customers when required and record actions and lessons learned to improve response.
Q: What low-cost actions can a small business implement in the first 30 days to improve AI security?
A: Use these AI safety tips for small businesses by enabling MFA or passkeys on email, finance apps, cloud storage, and AI tools, publishing a one-page AI policy and approved tools list, and training staff for about 20 minutes on safe prompts and phishing red flags. Also turn off chat history or model training where possible, review vendor settings, set automatic updates, run a full backup, and test a file restore.
Contents