Crypto
23 Sep 2026
Read 12 min
US-China AI safety summit 2026 How to Interpret Results *
US-China AI safety summit 2026 seeks narrow guardrails to secure stability without slowing innovation.
The US-China AI safety summit 2026 is set to focus on guardrails, not a slowdown. Xi Jinping and Donald Trump will push for safe development while competing for AI leadership. Expect talk of incident hotlines, risk reporting, and limited cooperation on high-risk uses, rather than any cap on model size or compute speed.
As world leaders gather, both governments want to keep building AI fast. Each side views the technology as a core part of national strength. Safety talks are on the agenda, but the pace of progress will not pause. Tech firms in China and the US are launching larger models, new chips, and huge data centers, even as they discuss common risk rules. That is the tension to watch as the US-China AI safety summit 2026 begins.
Alibaba said it is building a mega model that could reach 10 trillion parameters, rolling out what it calls China’s most powerful AI chips, and planning a 20-gigawatt data center push. One estimate ties that to as much as $160 billion in future cloud revenue.
Huawei moved faster to ship advanced AI chips that aim to replace Nvidia processors restricted by US controls.
Z.AI and Xiaomi showed how their AI systems can improve performance on their own, pointing to a trend toward more agentic and self-improving models.
Manus, an agentic AI startup, is seeking new funding to expand its platform after recent progress on business constraints.
The message is simple: China is closing the AI gap and building more of its own stack, from chips to data centers to models.
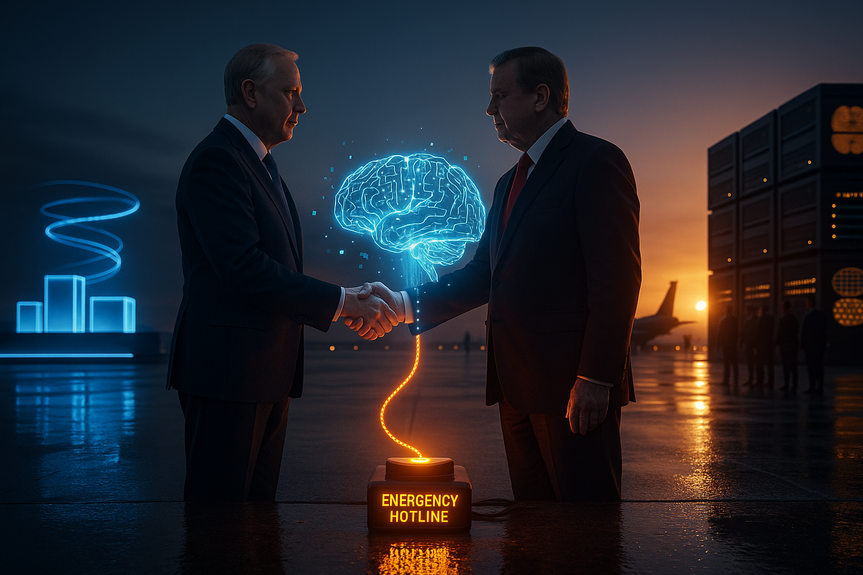
Incident hotline and rapid-response channel. A shared number and protocol could help manage cross-border AI incidents, such as major model misbehavior, fast-spreading deepfakes, or a discovered vulnerability in widely deployed systems.
Common risk language. A basic glossary for safety terms (for example, high-risk capabilities, misuse vectors, or containment) would help engineers and regulators talk in clearer ways.
Voluntary reporting for severe events. Companies may agree to confidentially report certain failures or dangerous capability findings to national points of contact, with a time limit and a scope that respects trade secrets.
Baseline evaluations. The sides might back neutral testing for high-risk areas like cyber intrusion assistance, bio threats, and autonomous tool use. Shared, minimal benchmarks would not reveal model IP but could prove that core safety checks exist.
Watermarking and provenance. Expect support for content provenance standards to mark AI-generated media and help fight election deepfakes and scams.
Model access controls. Firms may commit to stricter gating for tools that can write code, run agents, or trigger external actions, especially for anonymous or new accounts.
None of these items would slow the race. But they could cut obvious risks and create a way to talk during a crisis.
If the US tightens compute or export rules, global supply chains may shift again. Watch data center bookings, network hardware orders, and alternative chip demand.
If China shows progress in homegrown accelerators and system software, it can blunt the effect of controls and keep model scale growing.
Power and cooling constraints will matter as much as chips. A 20-gigawatt plan highlights how energy and land policy now define AI capacity.
Joint announcement of an AI incident hotline with target response times.
Agreement on a short list of severe risks with shared evaluation methods.
Timelines for company participation or pilot drills within 60–90 days.
Commitments to content provenance across major platforms ahead of key elections.
A general statement on the need for safe AI and continued dialogue.
Working groups to define terms and reporting formats, with no deadlines.
Encouragement for voluntary corporate actions but no tracking or metrics.
Vague language without mechanisms, timelines, or responsible agencies.
No mention of hotlines, incident drills, or joint evaluations.
Focus only on national positions and not on shared risk management.
Build incident reporting now. Even voluntary regimes reward teams that can show logs, red-team records, and structured postmortems.
Adopt provenance tools. Watermarking and content signatures are fast becoming table stakes for major apps.
Harden agent tools. Add stricter permissioning, monitoring, and kill switches for autonomous actions, especially for code and finance tools.
Plan for more evaluations. Expect requests to publish safety test results for sensitive use cases, even if standards stay minimal.
Expect compute scrutiny. If your roadmap depends on cutting-edge chips, diversify sources and model architectures that use compute efficiently.
Prepare for cross-border risk audits. Customers may ask for proof of safeguards that align with both US and Chinese expectations.
Which agencies run the hotline, and how companies plug in.
A pilot cross-border incident exercise and its public after-action report.
Any convergence on evaluation suites for cyber, bio, and agentic risks.
Movement on chip supply: domestic accelerators, packaging capacity, and data center power contracts.
Corporate updates on mega-model training runs, including parameter targeting and power footprints.
New commitments on deepfake labeling before major elections.
US-China AI safety summit 2026: What the meeting is really about
The core trade-off is clear. The US and China want safer systems, but they also want to win the race. Leaders will likely seek narrow guardrails that lower shared risk without hurting national advantage. This means dialogue on how to prevent misuse, not limits on how fast companies can train new models. Recent signals support this view. US officials have floated an emergency hotline for AI incidents and a standing channel for risk talks. China, which faces US chip export controls, has little reason to accept speed limits but does want stable rules on safety and markets. Both sides appear open to steps that help avoid accidents while keeping their edge.The tech backdrop: Momentum on both sides of the Pacific
China accelerates model scale, chips, and compute
In the days before the summit, major Chinese firms outlined big AI plans:The US doubles down on leadership
In the US, leaders dismiss calls to slow progress and stress the need to stay ahead. Major platforms push model upgrades, agent tools, and infrastructure scale. Washington also pursues rules to manage risks from advanced systems and to steer chip flows. Together, this shows commitment to both speed and security.What guardrails are likely on the table
Officials have not signaled a pause. Instead, they may aim for tactical steps that reduce the chance of harm. Based on public comments and prior international talks, watch for:The chip race and compute power remain the lever
Export controls on advanced chips remain a key policy tool for Washington. They aim to slow China’s access to top-tier compute, which is the fuel for frontier models. Beijing’s response is to develop replacements, increase domestic chip yield, and scale power and networking. That contest will shape who can train the largest models and how fast. For investors and builders, read the signals:How to read outcomes from the summit
As the US-China AI safety summit 2026 unfolds, focus on a few clear signals instead of long communiqués.Stronger-than-expected signals
Middle-ground signals
Weaker-than-expected signals
Implications for companies and researchers
Operational takeaways
Strategic takeaways
What to watch next
Bottom line
This summit is about safer speed, not slower speed. The likely outcome is a thin layer of shared safety steps that lower obvious risks while the race continues. Tech firms are already acting as if scale will keep rising. The best move now is to prepare for practical guardrails, better monitoring, and a sharper focus on high-risk uses. If leaders launch a real hotline and agree on basic evaluations, that will be progress. If not, companies should still raise their own bar. Either way, the US-China AI safety summit 2026 will shape how the world keeps building powerful systems with fewer surprises.(Source: https://finance.yahoo.com/technology/ai/articles/xi-trump-seek-safe-ai-070000935.html)
For more news: Click Here
FAQ
Q: What is the primary aim of the US-China AI safety summit 2026?
A: The summit aims to establish narrow guardrails that reduce shared AI risks while allowing both countries to continue rapid development and competition for leadership. Leaders are expected to prioritize practical measures like incident hotlines and risk reporting rather than imposing caps on model size or compute speed.
Q: Will the summit seek to slow AI development or cap model sizes and compute?
A: No, both Washington and Beijing have signaled they do not intend to slow AI development, and the summit is expected to produce guardrails rather than speed limits. Discussion will likely focus on cooperation for incident response and managing high-risk uses while permitting continued scaling.
Q: What specific guardrails are likely to be discussed at the US-China AI safety summit 2026?
A: Expect talks about an incident hotline and rapid-response channel, common risk language, voluntary confidential reporting for severe events, baseline evaluations for high-risk areas, watermarking and provenance standards, and stricter model access controls. These measures aim to cut obvious risks without slowing the overall race for AI leadership.
Q: How do chip export controls factor into the summit and AI competition?
A: Export controls on advanced chips are a central US policy tool intended to slow China’s access to top-tier compute and shape who can train frontier models and how fast. Beijing is responding by developing domestic accelerators and scaling chip production, making compute and packaging capacity a key lever in the competition.
Q: What recent actions by companies set the technological backdrop for the summit?
A: Chinese firms such as Alibaba (announcing a mega model up to 10 trillion parameters and a 20-gigawatt data center plan), Huawei, Z.AI, and Xiaomi have accelerated model scale, chips, and agentic features, while US platforms continue model upgrades, agent tools, and infrastructure expansion. This simultaneous scaling on both sides frames why talks focus on safety without pausing progress.
Q: What outcomes would signal a stronger-than-expected result from the talks?
A: Strong signals would include a joint announcement of an AI incident hotline with target response times, agreement on a short list of severe risks with shared evaluation methods, and timelines for company participation or pilot drills within 60–90 days. Commitments to cross-platform provenance standards ahead of major elections would also indicate meaningful progress.
Q: How should companies and researchers prepare for potential guardrails discussed at the summit?
A: Organizations should build incident reporting capabilities, adopt provenance and watermarking tools, and harden agent tools with stricter permissioning and kill switches for autonomous actions. They should also plan for more safety evaluations, diversify compute sources, and prepare for cross-border risk audits that align with both US and Chinese expectations.
Q: After the US-China AI safety summit 2026, how can observers interpret the results?
A: Observers should focus on concrete signals like whether a hotline is launched, whether shared evaluation methods are agreed, and whether pilot exercises or company timelines are set rather than lengthy vague statements. If those tangible steps appear it will be seen as progress; if not, companies and governments should still raise their own safety standards.
* The information provided on this website is based solely on my personal experience, research and technical knowledge. This content should not be construed as investment advice or a recommendation. Any investment decision must be made on the basis of your own independent judgement.
Contents